We hold ourselves to the standard we sell.
What we do to protect client data and source code, the attestations we hold, and how to report a vulnerability to us.
What we can show you
| SOC 2 Type II | Security, availability and confidentiality criteria. Audited annually; current report available under NDA. |
|---|---|
| Penetration testing | Independent external test of our corporate and delivery environments every six months, plus continuous internal testing by our own practice. |
| Cyber insurance | Carried at limits appropriate to our engagements; certificate available on request. |
| Background checks | All staff; additional screening for engagements that require it. |
| Framework alignment | Internal controls mapped to NIST CSF 2.0 and CIS Controls v8; CMMC Level 2 practices in place for defense-adjacent work. |
Your systems stay yours
- We work in your environment. Code lives in your repositories and runs in your cloud. We do not mirror client source to our systems.
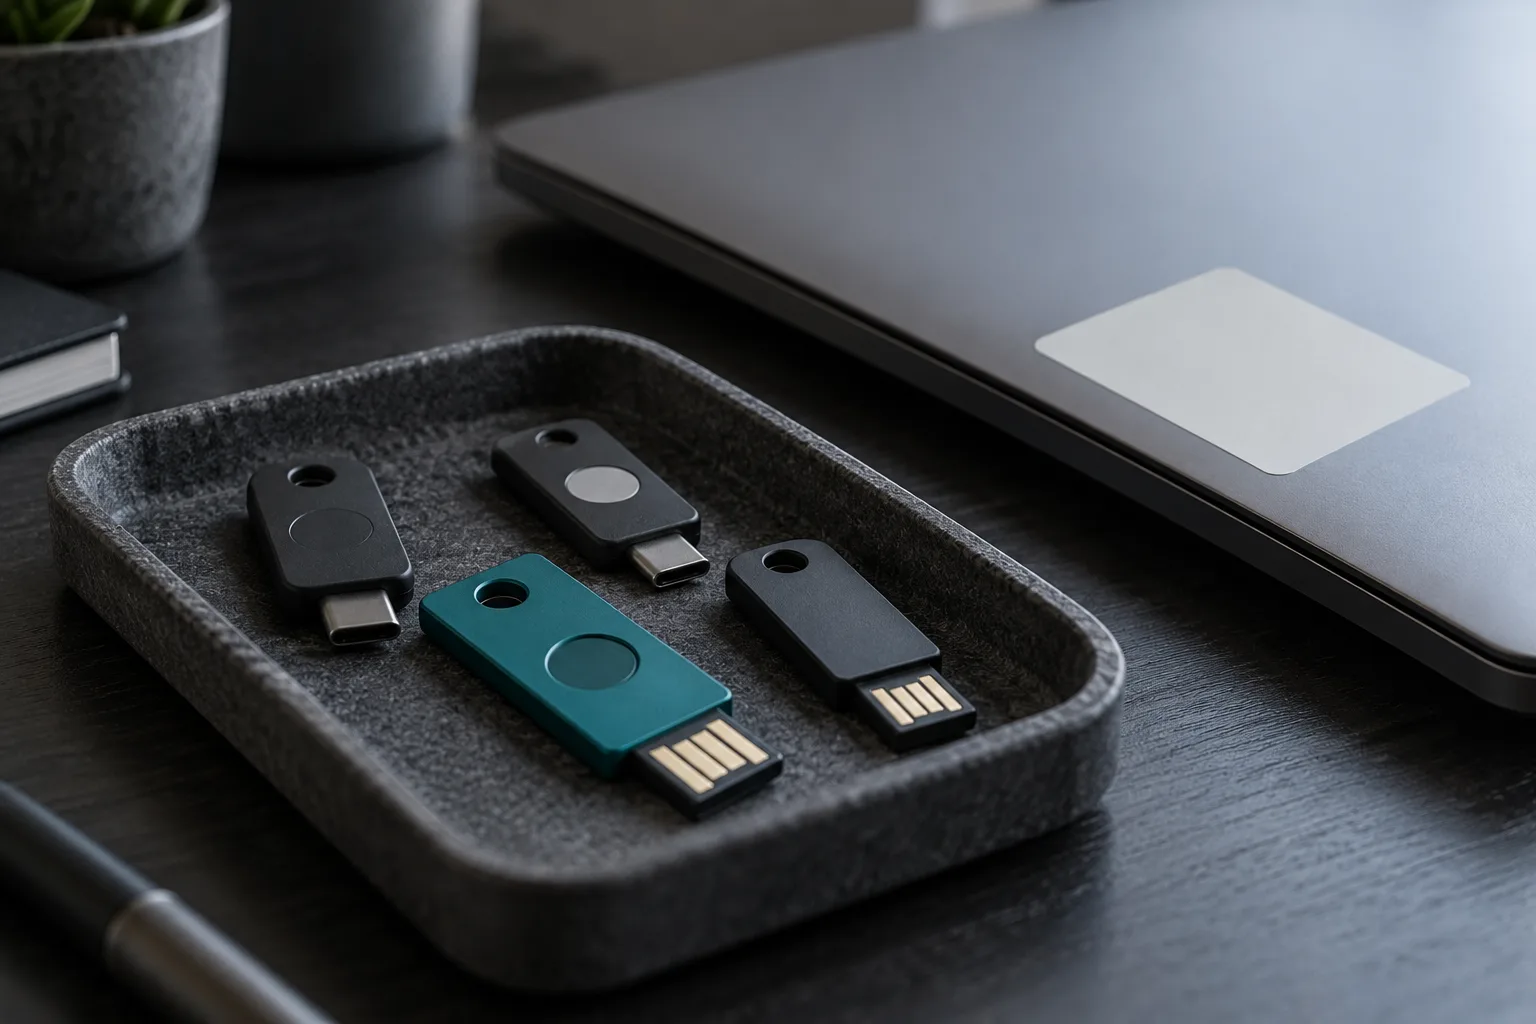
- Hardware-key access everywhere. Phishing-resistant MFA is required for every staff account, including ours into yours.
- Managed, encrypted endpoints. Every engineer's machine is company-owned, full-disk encrypted, monitored and wiped on departure.
- Segmented delivery environments. Engagements that require it get isolated workstations and networks run by our systems engineering function.
- Least privilege, reviewed quarterly. Access to client systems is granted per engagement and removed when it ends, with a record.
Run by a dedicated systems engineer
Our corporate and delivery infrastructure is owned by a dedicated systems engineer, not shared out among whoever is free. That role runs identity, endpoint management, network segmentation, backups, logging and the controls that our SOC 2 report describes, and sits inside the application security practice so that the people testing our clients also test us.
Backups are encrypted, offsite and restore-tested quarterly. Logs are centralized and retained for one year. Incident response is rehearsed twice a year with a tabletop that includes leadership.
Found something? Tell us.
We welcome reports of security vulnerabilities in our website, our corporate systems and software we publish. Email security@greyferrite.com. Our security.txt is published at the standard location.
What we commit to
- Acknowledge your report within two business days
- Keep you informed of progress and expected timelines
- Not pursue legal action against good-faith research that follows this policy
- Credit you publicly if you want it, once the issue is fixed
What we ask
- Do not access, modify or exfiltrate data that is not yours; stop and report as soon as you can demonstrate the issue
- No denial of service, social engineering of staff, or physical attacks
- Give us a reasonable period, normally 90 days, before public disclosure
- Client systems we build or operate are out of scope; report those to the client, or to us and we will route it
We do not currently run a paid bug bounty. We do say thank you, properly.